Bybit Discloses Malware Attack on macOS Users: Exploiting 'Claude Code' Malware to Launch Multi-Stage Intrusion
According to Bybit's official disclosure, its Security Operations Center (SOC) has discovered a sophisticated malware attack targeting macOS users. The attackers employed SEO poisoning to elevate a malicious website in Google search results. When users searched for the AI development tool 'Claude Code,' they were redirected to a fake installation page, triggering a multi-stage attack chain aimed at stealing credentials, encrypting assets, and gaining long-term control of the devices.
The attack was initially detected in March 2026. In the first stage, a Mach-O loader was used to deploy an osascript-based information stealer, exhibiting characteristics of the AMOS and Banshee families. This program could steal browser credentials, macOS keychains, Telegram sessions, VPN configurations, and encrypted wallet data, and it attempted to access 250+ browser wallet plugins and various desktop wallets.
The second stage involved a C++ backdoor program with sandbox detection and encryption configuration capabilities. It achieved persistence through a system-level proxy, received instructions via HTTP polling, and enabled remote control.
Bybit stated that its SOC utilized AI-assisted analysis in this incident, covering the entire process from sample classification and reverse engineering to IOC extraction and detection rule generation. This reduced the analysis time from several hours to about 40 minutes, enabling same-day detection and mitigation deployment, resulting in an overall efficiency improvement of around 70%.
David Zong, Chief Risk and Security Officer of Bybit Group, said, "As one of the early exchanges to publicly disclose such attack activities, we believe that sharing our findings contributes to enhancing the industry's overall defense capabilities. With an AI-assisted SOC, we have achieved the completion of threat detection and full attack chain visualization in a single cycle. Tasks that previously required multiple analysts working across shifts for reverse engineering, IOC extraction, report writing, and rule generation can now be completed in one session—AI handles a large portion of the analysis work, while analysts make judgments and validations. The future of security will enter the 'AI vs. AI' phase, where using AI to defend against AI will become a trend. Bybit will continue to increase its investment in security AI, driving threat detection towards minute-level response and automated intelligent handling."
The investigation also revealed that the attackers used fake macOS password pop-ups for social engineering attacks to steal user credentials and in some instances attempted to replace official wallets like Ledger Live and Trezor Suite with Trojan versions.
The attack targeted Chromium-based browsers, Firefox, Safari, Apple Notes, and local sensitive directories. The related malicious domains and C2 infrastructure have been addressed and publicly disclosed. The attack utilized intermittent HTTP polling communication to increase detection complexity.
Bybit pointed out that with the proliferation of AI tools, attackers are manipulating search results to target the developer community. As developers have access to code, infrastructure, and financial permissions, they have become high-value targets. Bybit confirmed the malicious infrastructure on March 12 and completed the analysis, detection, and mitigation measures on the same day. On March 20, they disclosed the incident to the public and released detailed protection guidelines.
Join the official Coincamps community:
Telegram: https://t.me/coin_camps
Recommended
Desk: Brent Crude Tops $110, Musk's Net Worth Drops 528.6 Billion in Four Days After Tesla Roadster Launch
Oct 17, 21:49
JST Fifth Buyback and Burn Successfully Concludes: Over 170 Million Tokens Worth Approximately $23.53 Million Burned, Buyback Mechanism Set for Comprehensive Upgrade
Oct 17, 20:10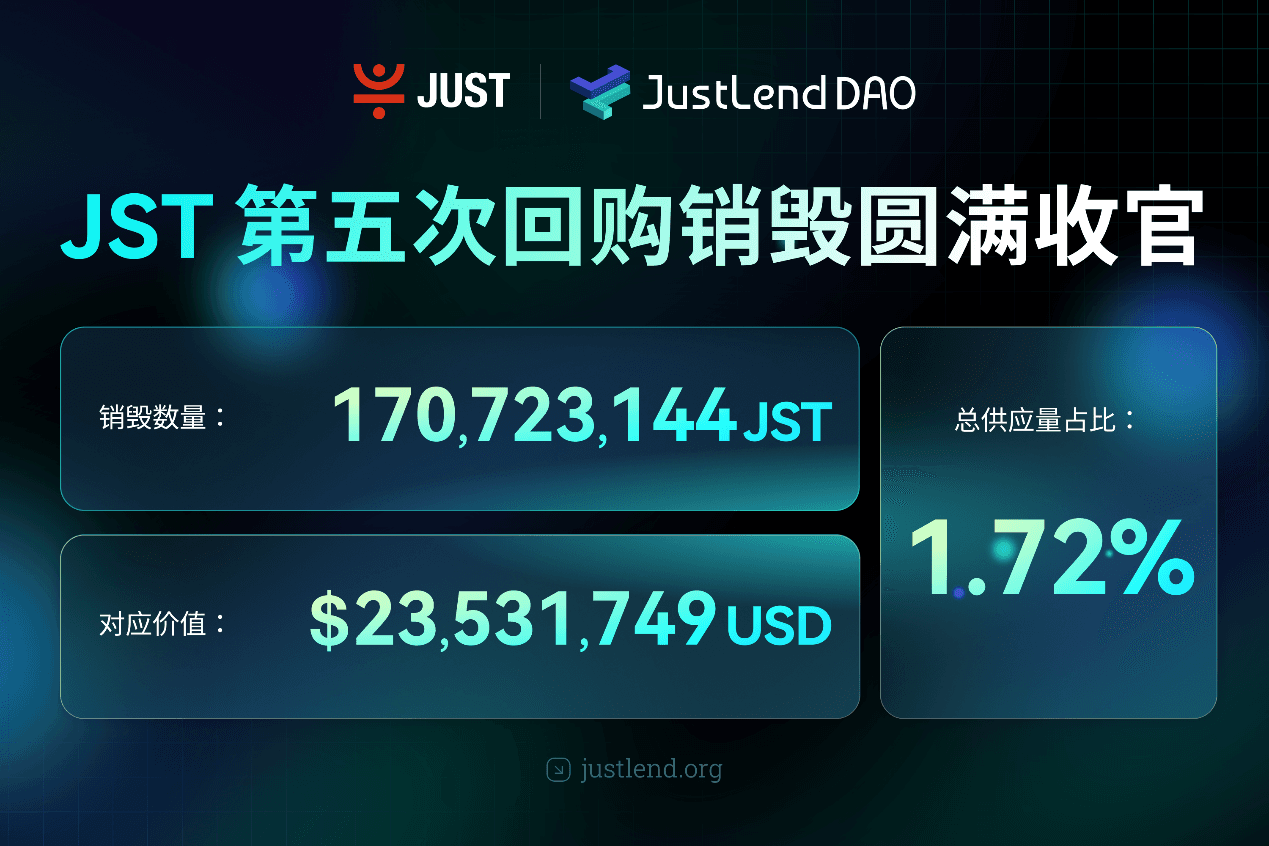
BitTorrent Brand Upgrade and Initial BTT Buyback & Burn Launch Simultaneously, Dual Engines Usher in New Era of Web3 Infrastructure
Oct 17, 20:00
Asia Market Daily: Japan's BOJ signals more rate hikes while Korea targets offshore perpetual platforms (2026/10/17)
Oct 17, 17:01Why did Papertrade backfire on you?
Oct 17, 17:01
The 'Strict Father' of Northern Myanmar: This Company Deploys 200,000 "AI Best Actors" to Strike Back Against Scammers
Oct 17, 15:34