Bitcoin's public key exposure may be the most critical topic to watch in 2027.

A few days ago, Ethereum core researcher Justin Drake called on the industry to prepare to enter "bunker mode" and move assets to new addresses whose public keys have not yet been exposed. He worries that mathematical breakthroughs brought by AI could cause ECDSA, a widely used digital signature algorithm, to face practical attacks before the quantum threat materializes. In the worst case, holders may have only months.
When prices fall, people can still discuss valuations and cycles. Once the security of private keys is called into question, the issue becomes: can the money in a wallet still truly be considered one's own? This shakes the very foundation of cryptocurrency.
The scenario Drake fears is that AI finds mathematical methods humans have not yet discovered, allowing attackers to recover wallet private keys from public information using existing hardware. He describes "cracking" quite specifically, for example using large GPU clusters to recover a target private key in about a week.
The quantum threat requires corresponding hardware capabilities. The risk brought by AI points to algorithmic breakthroughs: if a mathematical problem previously considered difficult to solve has a more effective method, the original computational cost will decline. Defenders were originally waiting for quantum computers, and now they also have to guard against changes in classical algorithms themselves.
Elliptic curves have rich mathematical structure, which is why Drake is especially worried about them. Could solutions humans have not yet found be discovered by more powerful AI? Can the security experience accumulated in the past still provide the same guarantees for the future?
Vitalik's response also takes this possibility seriously. He further extends the concern to lattice cryptography, including post-quantum schemes such as ML-DSA. These schemes also rely on specific mathematical problems being difficult to solve; if AI-accelerated research changes the solution methods, the security margin provided by existing parameters will also need to be reassessed.
Therefore, the label "quantum-resistant" is not enough to answer all AI risks. Vitalik prefers using hash constructions in applicable signatures and proofs to reduce dependence on complex mathematical structures. He also reminds that public-key encryption has harder-to-handle limitations and cannot directly follow this route.
There are also many people who oppose Drake's statement, with the main rebuttal being that Drake's claim of "months" is too alarmist.
NEAR founder Illia acknowledges that AI is challenging people's understanding of mathematical complexity, but he has not yet seen a substantial change in the timeline for practical attacks on elliptic curves. He is especially worried that complex migration operations will expose holders to new risks, and advocates making cryptographic replacement a routine capability.
Cryptography researcher Sean Bowe criticized the gap between the intensity of the warnings and the new evidence. Experts need to help non-expert holders deal with uncertainty; overly urgent language can leave people at a loss and also undermine the credibility of subsequent risk communication.
Public keys for 30% of BTC are already exposed
While it is still disputed when an attack might be feasible, the scale of assets that need to be addressed can already be measured.
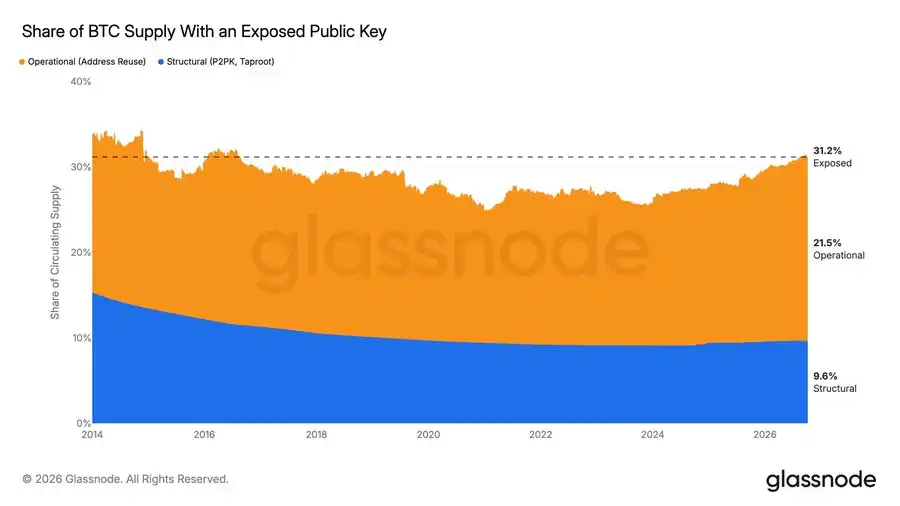
Glassnode researcher Rafael put the figure at about 6.26 million BTC whose corresponding public keys are already visible on-chain, accounting for 31.2% of issued supply, up from 24.8% in early 2021.
To understand why this portion of BTC is exposed, it is necessary first to distinguish between public keys and private keys.
Private keys are used to generate the digital signatures that authorize transfers, while public keys allow the network to verify signatures. Public keys being public is inherently consistent with the design of cryptographic systems, and security depends on an attacker finding it difficult to derive the private key from the public key. If a sufficiently powerful quantum computer changes that, already-public public keys would become attack material.
Some BTC addresses initially show only a hash digest of the public key on-chain, without temporarily revealing the public key itself. But when the holder spends funds, the public key is revealed. If the money is afterward still kept under the control of the same key, or if funds continue to be received there, those balances correspond to a public key that has already been exposed.
This is the exposure caused by address reuse. According to Rafael's tally, this portion amounts to about 4.33 million BTC. Moving funds to a suitable new address whose public key is still hidden behind a hash can reduce the current long-term exposure.
Another roughly 1.94 million BTC is different: the public keys are directly exposed by the script type. Early P2PK recorded public keys directly on-chain, and Taproot outputs also expose public keys. For this type of funds, even if they have not yet been spent, the public keys are already visible. Handling them requires considering the structure used by the address, not just whether the address has been used.
Exchanges are a relatively large actionable group. Among tagged exchange holdings, about 1.79 million BTC have visible public keys, accounting for 57% of these holdings, up from 55% in May. Since the May report, the overall exposed stock has increased by about 222,000 BTC, while net new BTC supply over the same period was only about 64,000 BTC.
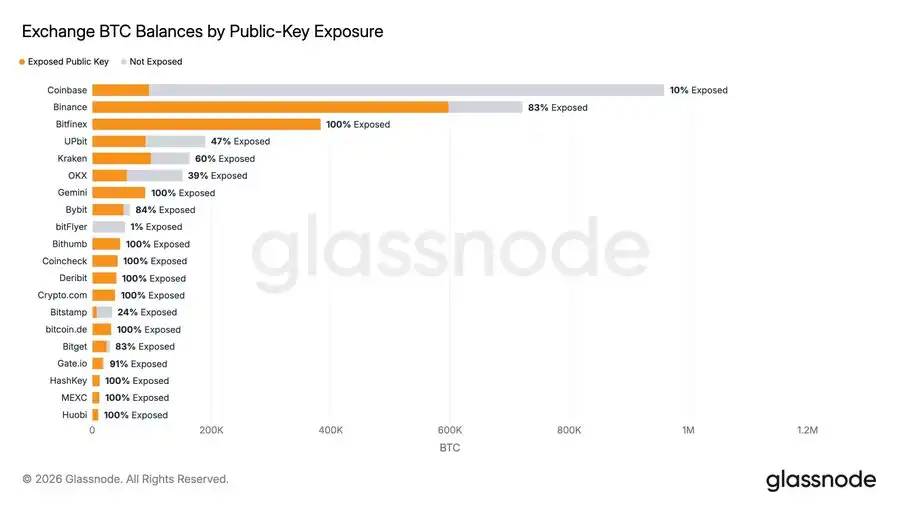
Reducing exposure still cannot replace a complete cryptographic upgrade. Funds whose public keys are temporarily hidden will still face an attack window in the future when they are spent and the public keys are revealed. But these data at least show that part of the industry's defensive work can be done in advance, and its progress can be observed.
Such uncertainty has already caused some investors to lose interest.
Trader metavestor stated on Twitter that they have already sold most of their spot holdings. They do not want to suspect every time they see new developments in AI mathematics research that they might suffer irreparable losses, nor do they want to see an ancient Bitcoin address transfer and wonder whether the private key has already been cracked.
They originally entered Crypto as a technological optimist, but now prefer to focus on AI and biotechnology. Continuing to hold Crypto makes them feel like they are shorting AI progress. Even if they miss the next bull market, they are willing to accept it; there are other assets available for trading.
"Banks also rely on cryptography" did not eliminate their concerns. In a follow-up explanation, they emphasized banks' security teams and defense capabilities, and also pinned hopes on recourse after major attacks and government bailouts. For on-chain assets, they lack the same confidence.
An attack does not need to simultaneously disable all cryptographic systems. As long as the cost of recovering the private key of a certain address is lower than the value of the assets that can be obtained, attackers have an incentive to try. Whether assets are easy to transfer away, whether attacks are easy to cash out, and whether losses can be recovered will all affect the distribution of risk.
However, there is a counterargument that BTC also faced existential risks in its early days, such as custody, adoption, and regulation, and investors' willingness to bear these risks is precisely part of the source of returns. The existence of risk alone cannot determine whether an asset is worth holding.
Counterarguers also do not agree that government bailouts can be regarded in advance as a guarantee. If trusted institutions generally come under greater attack pressure, the relative value of permissionless money still has room for reassessment. In the view of the counterarguers, Drake's warning will prompt the industry to take preventive measures more seriously, and this change may ultimately turn out to be a good thing.
Some are willing to bear risks that are still difficult to quantify, while others believe the energy cost of continuously monitoring them has exceeded the expected returns.
However, from an individual decision to exit to judging that the entire industry has no future, there is still a need to assess what defenders can do.
Crypto already has some concrete measures to address the threat.
Ethereum's EIP-8141 proposal attempts to make account verification programmable, allowing accounts to choose how to confirm transaction authorization and reducing dependence on fixed signature algorithms. According to binji, a member of the Ethereum Foundation, the subsequent roadmap also includes the goal of a minimally viable quantum-resistant L1.
The significance of this kind of cryptographic agility is to leave room for the system to switch verification methods. Long-term asset holding does not have to mean forever relying on a set of algorithms chosen today.
Solana's Jacob Creech introduced a recovery path based on secret seeds. Signing keys are derived from seeds, and he hopes legitimate holders can prove they know the seed through a hash proof, then migrate to a new signature scheme.
The NEAR account model described by Illia also emphasizes key management and rotation. According to his introduction, NEAR already supports ML-DSA and plans to add hash-based schemes. Combined with Vitalik's concerns about lattice cryptography, being able to continue adjusting authentication methods is inherently more valuable than merely promising that a certain algorithm is secure.
These paths do not yet guarantee that all funds can complete the upgrade in time. Wallets need to be compatible with new verification methods, institutions need to arrange custody migration, and holders need to preserve their assets during the process. Vitalik specifically warned that he personally has lost more money through failed migrations than through hacker attacks. Defense needs to factor in these costs as well.
But AI capabilities will also enter the defensive side. binji mentioned that AI can accelerate cryptographic research and also assist with formal verification, allowing implementations to undergo stricter scrutiny. Stronger tools can help find attack methods, but can also help discover errors and test new schemes.
AI will also enhance impersonation, deception, and social engineering attacks. Even if cryptography is strong enough, people with key permissions will still be targeted. A system that can update its security foundation while reducing the impact of any single person or institution being compromised still has utility in the face of stronger AI.
This is also the reason for remaining relatively optimistic. Technological progress will simultaneously change attack capabilities, defense capabilities, and people's demand for trustworthy systems. One cannot simply fix the latter two and extrapolate attackers' progress all the way to the endgame.
Following these changes, cryptographic upgrades and custody migration will become important themes in 2027.
The sense of security in Crypto needs to be rebuilt. A system that can continuously update its security foundation and reduce the concentration of key permissions will only become more valuable in the AI era.
Join the official Coincamps community:
Telegram: https://t.me/coin_camps
Recommended
Tian Keyu swore that lying would result in "lifelong research setbacks."
Oct 13, 18:06
Interview with NEAR Co-founder Illia: Integrating with NASDAQ, Launching Quantum-Resistant Features, Why Is NEAR Considered the Ethereum of This Bull Market?
Oct 13, 18:03
Latest Ruling in the Qian Zhimin Case: 61,000 Bitcoins Surge 200-Fold, Chinese Victims May Only Recover Their Principal
Oct 13, 17:00
$20 billion short: How OpenAI's revenue controversy is shaking up the AI market
Oct 13, 16:04
Institutional Interpretation: Why Can't Hyperliquid Compete with Polymarket in Prediction Markets?
Oct 13, 15:58
Morgan Stanley Research Analysis: Samsung Leads Global Profit Rankings, Yet Memory Super Cycle Remains Hard to Fully Value
Oct 13, 15:37