Bitget Hacker Turns to Zcash Privacy Pool: Where Are the Stolen Funds Going After Near Rejects $50M Coin Swap?
Compiled: TechFlow
TechFlow Summary: The money laundering trail for the Bitget $387.5 million hack is unfolding in real time—Near Intents has loudly declined to process involved swaps, while Thorchain continues to permit them citing "decentralization," and hackers have already begun moving part of the illicit proceeds into Zcash privacy pools. The choice decentralized protocols face between maintaining a "permissionless" network and implementing a "denial of service" is being thrust into the spotlight by this incident.

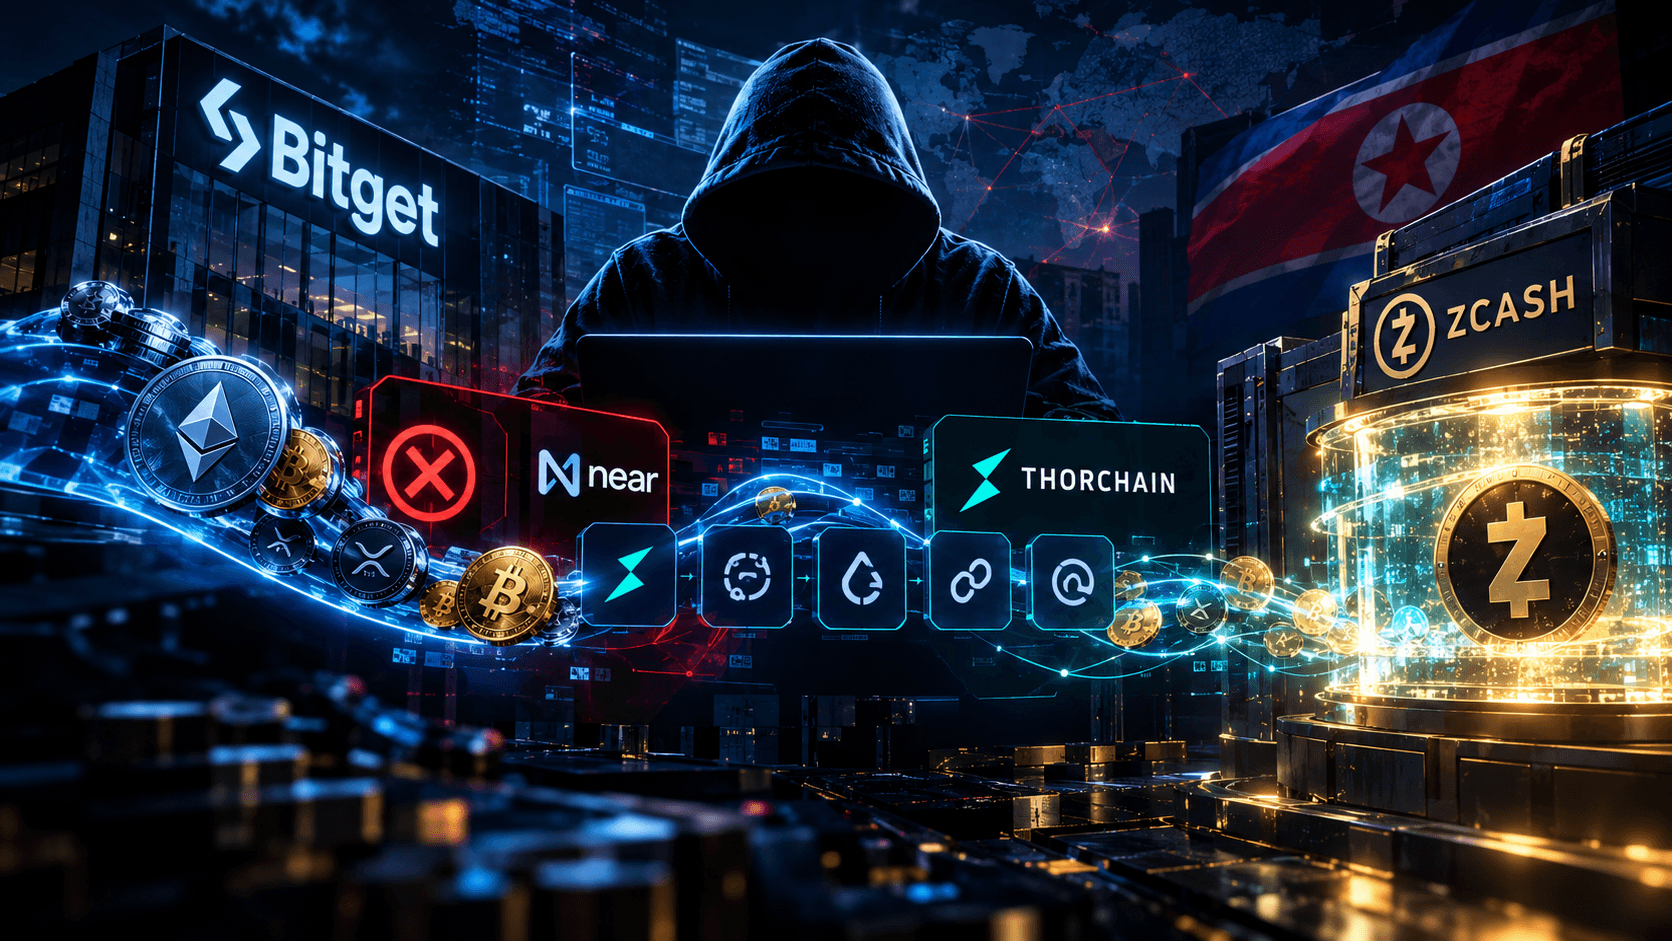
Hackers behind the Bitget $387.5 million theft are now hiding part of the stolen funds in Zcash privacy pools. On-chain investigator ZachXBT stated on Wednesday that attackers began transferring approximately 2,700 ZEC—worth around $3.8 million—to Ironwood, a shield pool on the privacy-focused blockchain Zcash.
Shield pools are a feature of the Zcash network that encrypt the sender, receiver, and transaction amount, meaning once funds enter, their destination cannot be traced. Ironwood launched on July 28 to replace the older Orchard pool. Researchers had previously discovered a vulnerability in Orchard that could potentially allow counterfeit coins to be minted.
According to on-chain tracking, this deposit accounts for roughly one-seventh of the ZEC stolen in the hack. Investigators can still see tokens entering and leaving the pool, but cannot monitor what happens in between.
Bitget CEO Gracy Chen previously noted that the attack's IP addresses and patterns align with North Korean hackers. Blockchain analytics firm Elliptic also rates the likelihood of North Korean involvement as "very high." Elliptic has further listed this case as the largest suspected North Korean heist of 2026, pushing the year's total past the $1 billion mark.
How the Funds Reached This Stage
The theft began on September 24, when Bitget's systems flagged unauthorized outgoing transactions from its hot wallet—a wallet connected to the internet used to hold the exchange's daily operational funds. Chen stated that attackers compromised the backend systems and forged transaction data rather than stealing private keys. Bitget confirmed that its protection fund covered the losses, leaving customer balances unaffected.
This was followed by the money laundering phase. TRM Labs found that attackers split the funds across multiple new wallets, each holding round sums of approximately 10,000 ETH or 20 million XRP. Smaller amounts were routed through cross-chain swap services—tools that allow token exchanges across different blockchains to obfuscate fund trails—utilizing platforms such as Thorchain, Across, Bridgers, Chainflip, and FixedFloat.
In the meantime, Near Intents pushed back. General Manager Alex Shevchenko said Tuesday that its screening system named SHIELD blocked over $50 million in swap requests linked to the Bitget attackers. He noted that approximately $503,000 was frozen during the swap process, while about $166,000 slipped through.
Near stated that the frozen funds will proceed through legal and recovery channels. This move ignited longstanding debates within the crypto community regarding the term "permissionless"—which implies that anyone can use the network without approval. Near co-founder Illia Polosukhin argued that this does not mandate that every application must process every single transaction.
Thorchain took a different approach. After Chen publicly demanded they refuse service to the attacker addresses, Thorchain posted on X stating that a network halt is an emergency tool to protect the protocol, rather than a mechanism to freeze specific funds or blocks swaps. Its developers noted that the network is run by independent node operators who vote on halting operations, rather than decisions being made by a single company.
A prominent question remains whether Thorchain has halted trading before. According to its own reports, following a $10.7 million exploit on May 15, it paused the entire network for roughly five weeks before resuming operations on June 22.
During that period, the hackers' swapping operations continued. On Monday, on-chain data showed that several batches totaling approximately 2,390 ETH—worth around $6.3 million—were converted into 75.2 BTC via Thorchain.
Bitget offers a bounty: 5% of any frozen funds and 5% of any recovered funds, excluding actions mandated by courts or law enforcement agencies.
Join the official Coincamps community:
Telegram: https://t.me/coin_camps
Recommended
Hyperliquid will use $15 million USDC revenue for HYPE buybacks; buybacks will no longer rely solely on trading fees.
Oct 3, 18:27
Grayscale Zcash Spot ETF Sees $93.56M in Single-Week Redemptions: Honeymoon Period Turns Sharp, Once Held Nearly 3.5% of Supply
Oct 3, 16:41
After resuming withdrawals, funds did not fall but rose instead. How did Bitget turn the situation around in five days?
Oct 3, 16:32
SEC Clears 3x Leveraged Bitcoin and Ethereum ETPs: Listing Rules Approved, Trading Still Pending Activation
Oct 3, 16:22
Funds Rose Instead of Fell After Withdrawals Were Resumed: How Did Bitget Turn Things Around in Five Days?
Oct 3, 16:11
CryptoPunks Trading Volume Surges Nearly 12X in a Week: Rare Variants Sell for Millions Again, Market Rally Decoupled from ETH
Oct 3, 13:36